Swansea University Audit Exposes Cookie Consent Failures on UK Gambling Platforms
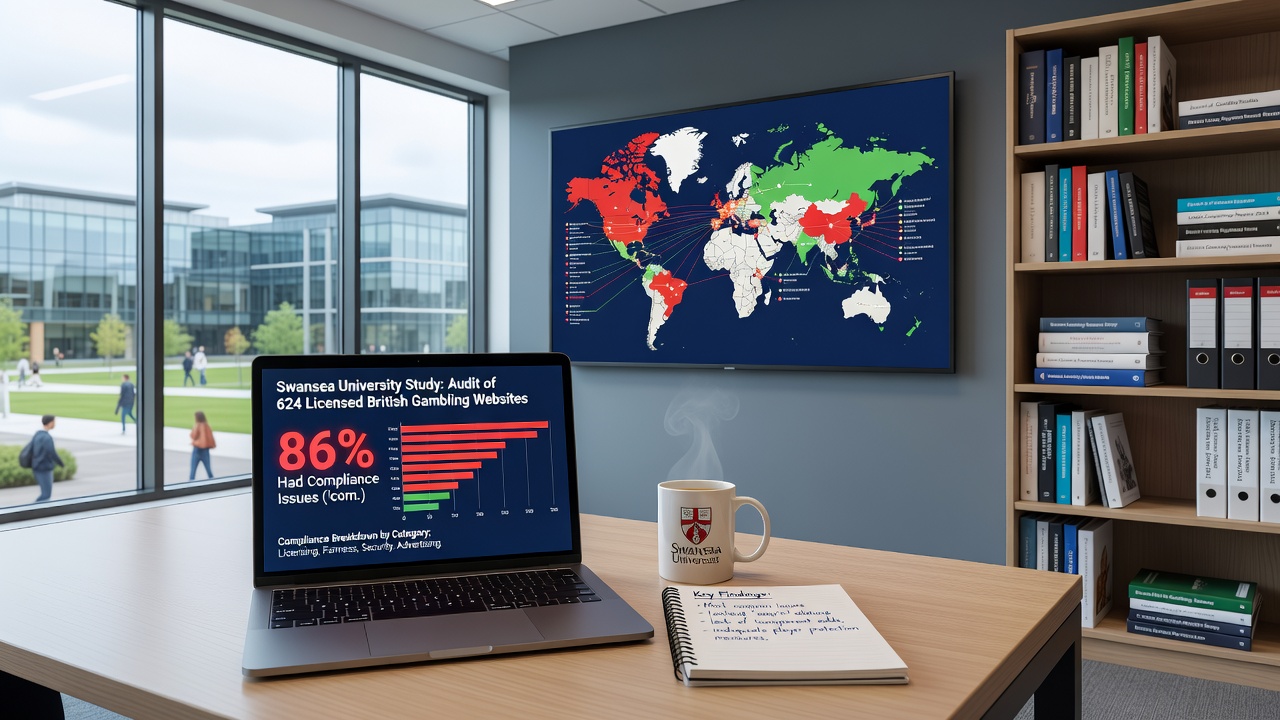
Researchers at Swansea University conducted a detailed audit of 624 licensed British gambling websites and discovered that 86 percent of them committed at least one GDPR breach tied directly to cookie consent banners along with related data collection practices, while a separate broader study of websites overall recorded a violation rate of 54 percent.
The audit examined how these sites handle user data through tracking technologies, and the results highlighted consistent patterns of noncompliance that exceeded the rates found across general web platforms.
Audit Methodology and Core Findings
Teams reviewed each site for compliance with GDPR requirements on consent mechanisms, and they identified specific issues such as the absence of any option to disable tracking on 24 percent of the platforms examined, pre-consent data collection occurring on two-thirds of the sites with frequent transmission of that information to third-party analytics providers, and widespread deployment of dark patterns that featured pre-selected invasive settings by default.
These practices occurred even though GDPR rules require clear, affirmative consent before personal data processing begins, and the study documented how many sites collected identifiers and behavioral signals without offering users meaningful choices at the outset.
Breakdown of Specific Violations
One category involved sites that presented cookie banners without any reject button, which forced users either to accept all tracking or navigate away entirely, while another common issue appeared when banners loaded tracking scripts immediately upon page view before any consent interaction took place.
Dark patterns took multiple forms including toggles set to allow maximum data sharing by default, confusing language that obscured the scope of third-party sharing, and repeated prompts designed to encourage acceptance after an initial rejection attempt.
Data sent to third parties often included device fingerprints and browsing histories routed to advertising networks and analytics firms, and the audit noted that these transfers happened without the required legal basis in a majority of the sampled domains.
Comparison With Broader Website Studies
The 86 percent violation rate among gambling sites stands notably higher than the 54 percent figure reported in a wider examination of websites across multiple sectors, which suggests that the combination of high traffic volumes and reliance on targeted advertising may create stronger incentives for aggressive data collection in this particular industry.
Researchers cross-referenced their results against earlier compliance surveys and found that the gambling sector showed elevated rates in every measured category of consent failure, particularly in the use of pre-ticked boxes and the speed at which tracking activated before user input.
Regulatory Context and Enforcement Landscape
UK data protection authorities have issued guidance requiring explicit consent for non-essential cookies, yet the audit revealed that many operators continued to operate outside those parameters at the time of testing, and the study authors compiled their observations into a report that regulators could use for further investigation.
The findings were first highlighted in coverage from The News International, which summarized the Swansea University results and placed them alongside ongoing discussions about enforcement priorities in the online gambling market.
Technical Details of Data Flows
Analysis of network requests showed that two-thirds of the audited sites initiated calls to external domains carrying user data before any consent banner received interaction, and these calls frequently transmitted IP addresses, browser configurations, and session identifiers to services operated by major technology companies.
Consent management platforms installed on many sites failed to block these transmissions until after acceptance occurred, which created a window during which data left the site regardless of user preference.
Conclusion
The Swansea University audit provides a clear snapshot of current consent practices across hundreds of licensed UK gambling domains, and the documented breach rate of 86 percent indicates that substantial work remains before these platforms align fully with GDPR standards on cookie handling and data sharing. The detailed breakdown of violation types offers regulators and operators concrete areas for targeted improvements in banner design, script loading sequences, and default settings.